Background of How Hackers Read Assembly Code Control Flow Stack Frames Manual Decompilation
Looking for the latest information on How Hackers Read Assembly Code Control Flow Stack Frames Manual Decompilation? We've compiled comprehensive data, records, and insights about How Hackers Read Assembly Code Control Flow Stack Frames Manual Decompilation.
Core Information
Explore the key sources for How Hackers Read Assembly Code Control Flow Stack Frames Manual Decompilation.
Latest News
Stay updated on How Hackers Read Assembly Code Control Flow Stack Frames Manual Decompilation's newest achievements.
How to Learn Assembly Language (For Hackers)
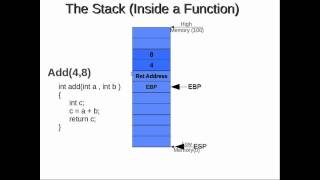
Assembly Programming Assembly Function Stack Frame Explained
Learn Assembly for Game Hacking in 2025
you can learn assembly in 10 minutes (try it RIGHT NOW)
How to Learn Assembly Language (For Hackers)
x86 Assembly for Beginners | Registers, Memory, Stack & Reverse Engineering Explained
ASSEMBLY HACKING LIVE! x86 Assembly, Reverse Engineering & PicoCTF
DFA and code control flow obfuscation a real world example Dima Kovalenko
Exploiting Stack 5 from Protostar on ARM (Azeria-Labs)
Data is compiled from public records and verified media reports.
Last Updated: September 20, 2026
Conclusion
For 2026, How Hackers Read Assembly Code Control Flow Stack Frames Manual Decompilation remains one of the most searched-for information profiles. Check back for the newest reports.
Disclaimer: Disclaimer: All information is compiled from publicly available data, media reports, and analysis. Actual details may vary.