Background to Using Gitlab Application Security Capabilities With Jenkins Devsecops
Looking for the latest information on Using Gitlab Application Security Capabilities With Jenkins Devsecops? We've researched comprehensive data, records, and insights about Using Gitlab Application Security Capabilities With Jenkins Devsecops.
Important Facts
Explore the key sources for Using Gitlab Application Security Capabilities With Jenkins Devsecops.
History
Stay updated on Using Gitlab Application Security Capabilities With Jenkins Devsecops's newest achievements.
How to Build a DevSecOps Pipeline in Jenkins - Part 2 of 2
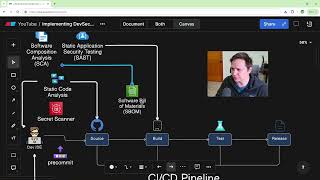
How to Create a DevSecOps CI/CD Pipeline
Jenkins CI triggering GitLab Security Scans on Success - Demo
Accelerate AppSec Efficiency with the GitLab Security Dashboard (DevSecOps)
🔎 Insider Threats in GitLab, Jenkins & K8s (by Michał El Fartas) | Cloud & CI/CD Security TechSpot
How to Integrate Container Image Scanning in GitLab CI/CD Pipeline | DevSecOps Best Practices
DevSecOps Project | CI/CD Pipeline with Jenkins | Secure Your Code with SonarQube and Trivy
A tour of GitLab Security capabilities
DevSecOps Automation Using GitLab and AWS
DAST with Jenkins: Scan & Reporting with OWASP ZAP
Full Guide
Data is compiled from public records and verified media reports.
Last Updated: September 20, 2026
Future Outlook
For 2026, Using Gitlab Application Security Capabilities With Jenkins Devsecops remains one of the most talked-about information profiles. Check back for the latest updates.
Disclaimer: Disclaimer: All information is compiled from publicly available data, media reports, and analysis. Actual details may vary.